Collection
Device and OS Customization
2026.09.15
The Long-Standing Debate Surrounding Nintendo Device Modifications
Exploring the Boundaries of Preservation and Unauthorized Use Through DS, Wii, 3DS, and Switch
Nintendo devices have offered unique controls and portability across generations, generating significant interest in preserving games even after discontinuation. However, issues surrounding flash carts, unauthorized software, and online sanctions have continued to emerge. We summarize the differences based on actual products from DS Lite to Switch Lite.
Nintendo's terms of use warn that unauthorized modifications or devices may render the console and software unusable after updates. Instead of detailing specific bypass procedures, we check the risks and official alternatives. Since official policies and device-specific support may change, it is safer to verify manufacturer guidance before use.
Nintendo's terms of use warn that unauthorized modifications or devices may render the console and software unusable after updates. Instead of detailing specific bypass procedures, we check the risks and official alternatives. Since official policies and device-specific support may change, it is safer to verify manufacturer guidance before use.
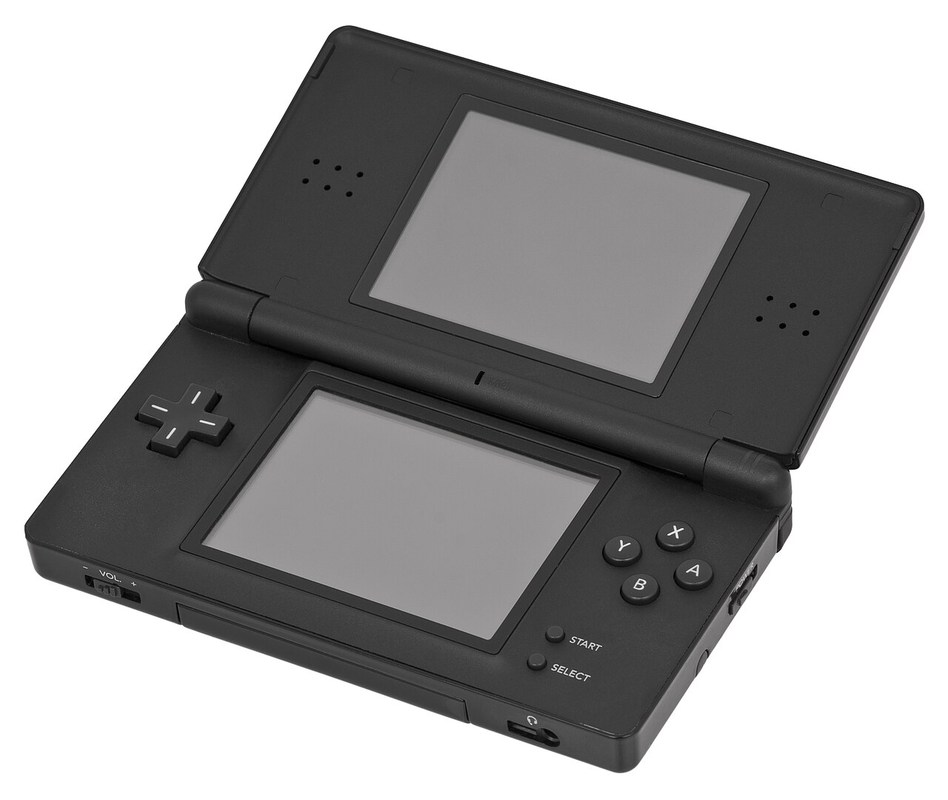
Nintendo DS Lite
The Nintendo DS Lite is a portable gaming device released by Nintendo. The key year of focus here is 2006, and the context of device modification involves the debate surrounding flash carts and unauthorized software. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The first risk to consider is copyright infringement and data corruption. Unauthorized changes may not only lead to update failures or data loss but also impact financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check genuine cartridges and official compatibility information. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The first risk to consider is copyright infringement and data corruption. Unauthorized changes may not only lead to update failures or data loss but also impact financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check genuine cartridges and official compatibility information. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 휴대형 게임기
제조사 Nintendo
관련 시기 2006년
주요 위험 저작권 침해와 저장 데이터 손상
공식 대안 정품 카트리지와 공식 호환 정보
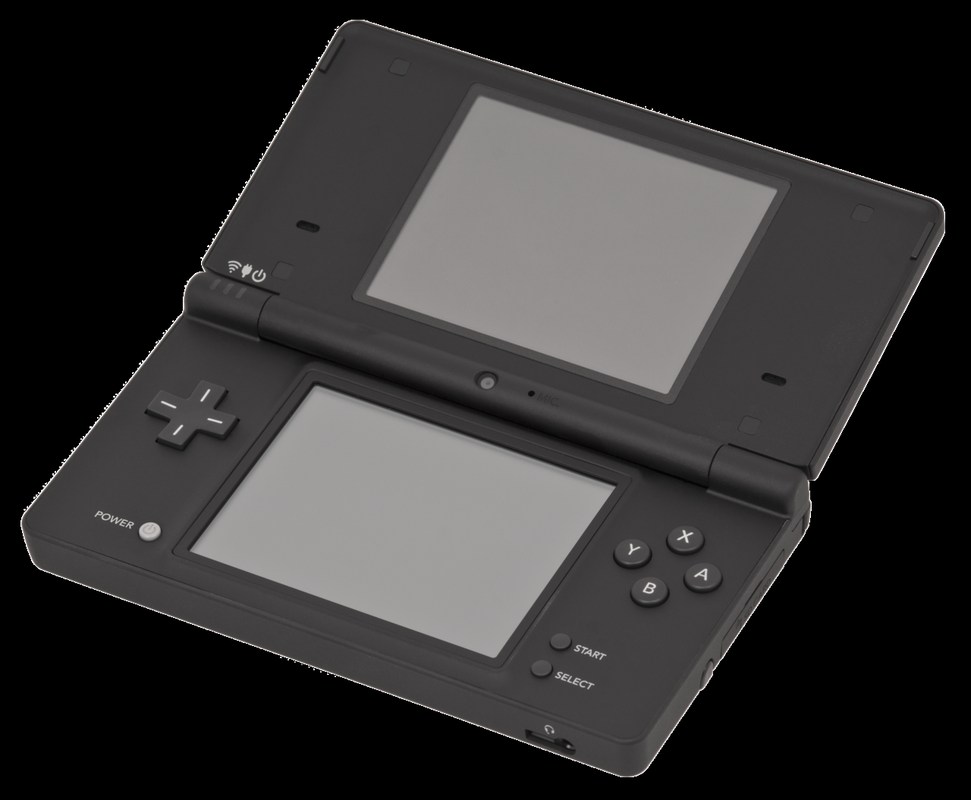
Nintendo DSi
The Nintendo DSi is another portable gaming device released by Nintendo. The key year of focus here is 2008, and the context of device modification pertains to the introduction of download features and the resulting interest in system modifications. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The primary risks to consider are update conflicts and functionality halts. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official system settings and purchase history management. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The primary risks to consider are update conflicts and functionality halts. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official system settings and purchase history management. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 휴대형 게임기
제조사 Nintendo
관련 시기 2008년
주요 위험 업데이트 충돌과 기능 정지
공식 대안 공식 시스템 설정과 구매 이력 관리
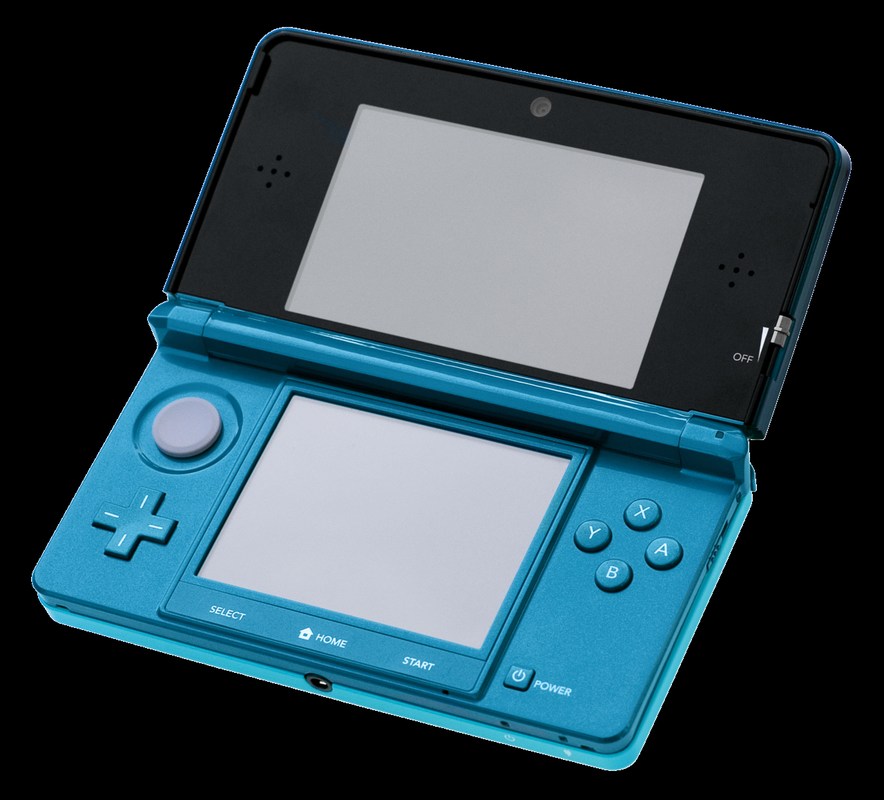
Nintendo 3DS
The Nintendo 3DS is a portable gaming device released by Nintendo. The key year of focus here is 2011, and the context of device modification involves regional restrictions and preservation demands after discontinuation. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The primary risks to consider are account, online, and saved data risks. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check genuine software and data transfer options. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The primary risks to consider are account, online, and saved data risks. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check genuine software and data transfer options. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 휴대형 게임기
제조사 Nintendo
관련 시기 2011년
주요 위험 계정·온라인·저장 데이터 위험
공식 대안 정품 소프트웨어와 데이터 이전
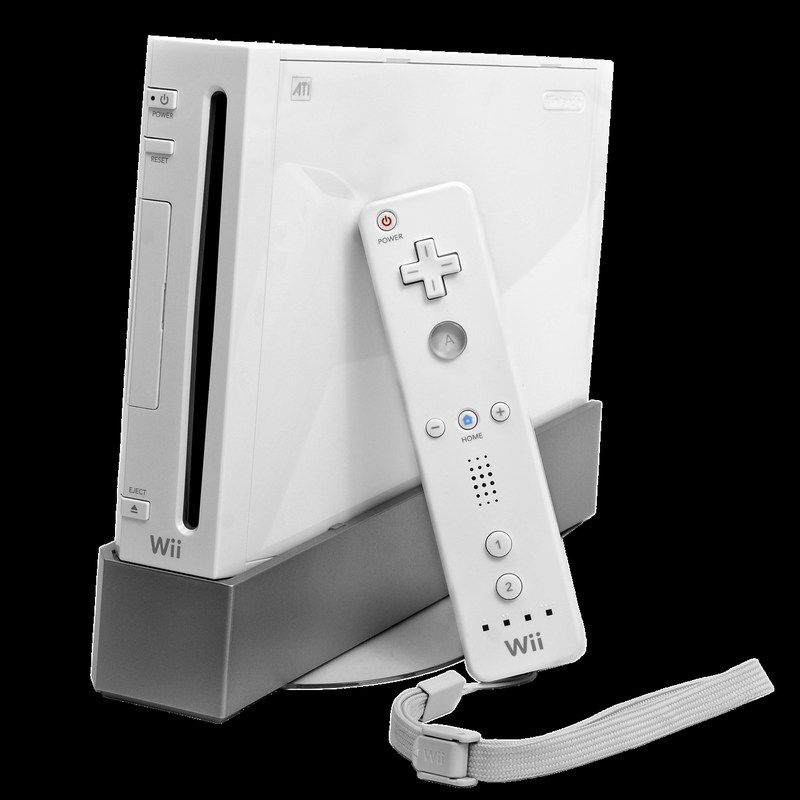
Wii
The Wii is a home console introduced by Nintendo. The key year of focus here is 2006, and the context of device modification involves the homebrew culture that flourished around motion gaming. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The primary risks to consider are bricking and copyright issues. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official discs and compatible peripherals. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The primary risks to consider are bricking and copyright issues. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official discs and compatible peripherals. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 거치형 게임기
제조사 Nintendo
관련 시기 2006년
주요 위험 벽돌 현상과 저작권 문제
공식 대안 공식 디스크·호환 주변기기
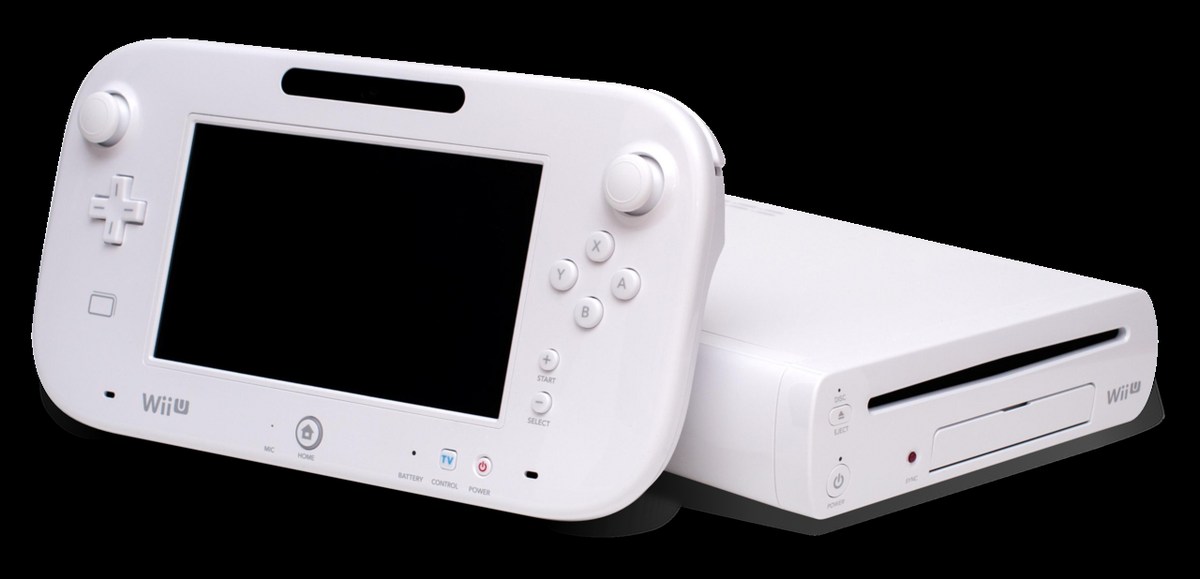
Wii U
The Wii U is a home console introduced by Nintendo. The key year of focus here is 2012, and the context of device modification involves discussions on preserving discontinued platforms and unauthorized modifications. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The primary risks to consider are system updates and storage device conflicts. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official data transfer and compatibility lists. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The primary risks to consider are system updates and storage device conflicts. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official data transfer and compatibility lists. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 거치형 게임기
제조사 Nintendo
관련 시기 2012년
주요 위험 시스템 업데이트와 저장장치 충돌
공식 대안 공식 데이터 이전 및 호환 목록
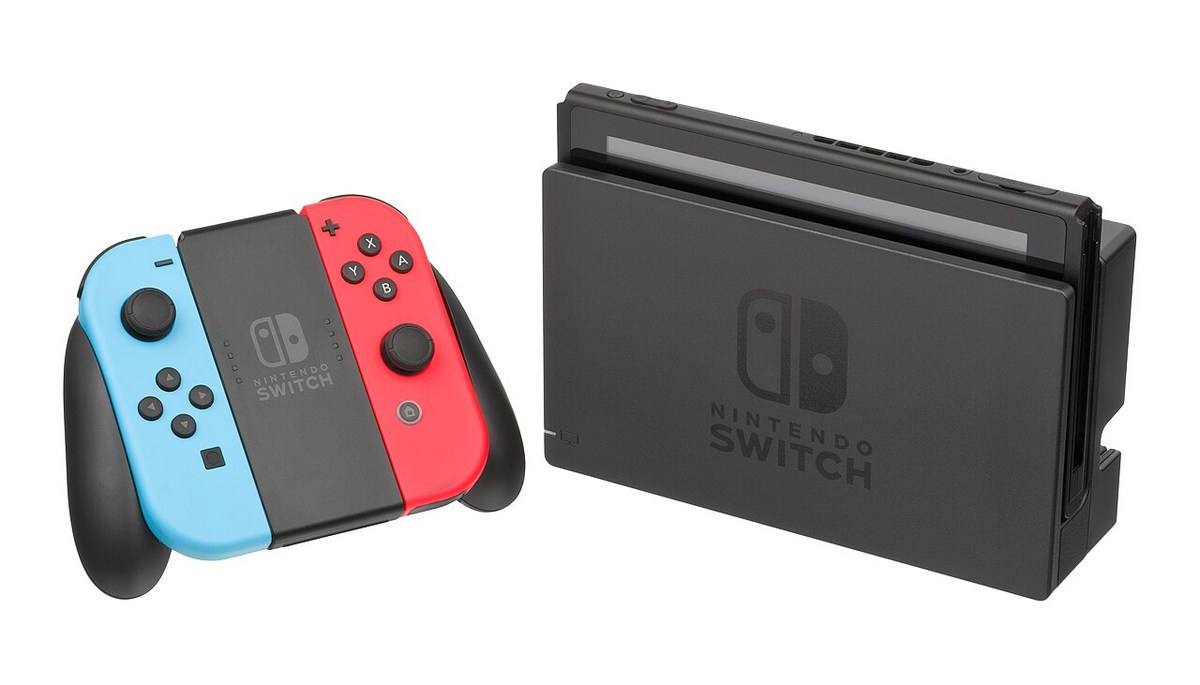
Nintendo Switch
The Nintendo Switch is a hybrid gaming device introduced by Nintendo. The key year of focus here is 2017, and the context of device modification involves hardware generation differences and debates surrounding online restrictions. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The primary risks to consider are console inoperability, account restrictions, and copyright risks. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official eShop, parental controls, and accessibility settings. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The primary risks to consider are console inoperability, account restrictions, and copyright risks. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official eShop, parental controls, and accessibility settings. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 하이브리드 게임기
제조사 Nintendo
관련 시기 2017년
주요 위험 콘솔 사용 불능·계정 제한·저작권 위험
공식 대안 공식 e숍·자녀 보호·접근성 설정
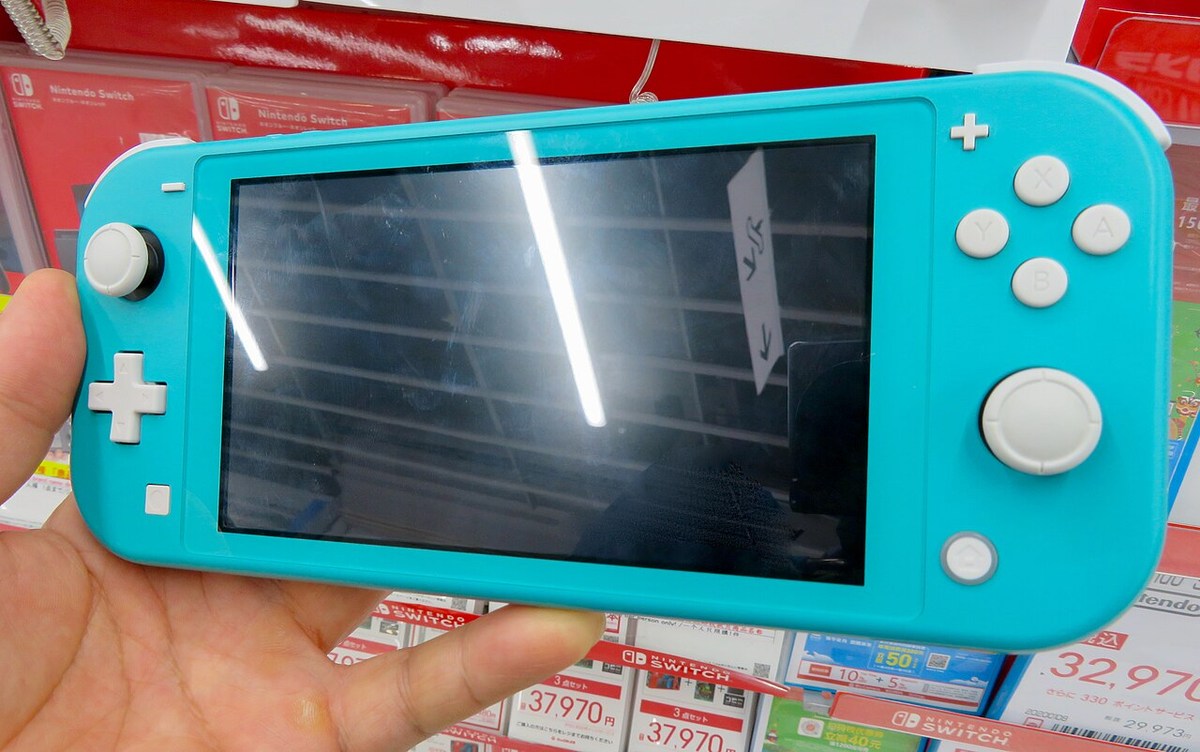
Nintendo Switch Lite
The Nintendo Switch Lite is a portable gaming device introduced by Nintendo. The key year of focus here is 2019, and the context of device modification revolves around the interest in repairs and modifications within its handheld-only structure. Although the term 'jailbreak' is used, bypassing iOS authority restrictions, changing the Android bootloader state, and executing unauthorized code on consoles differ in technical and terms of service meanings. Thus, explanations that do not distinguish between device names, generations, and operating system versions cannot serve as grounds for assessing the current state.
The primary risks to consider are warranty exclusion, online restrictions, and device damage. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official repairs and cloud data options. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
The primary risks to consider are warranty exclusion, online restrictions, and device damage. Unauthorized changes may lead to update failures or data loss and may also affect financial/authentication apps, cloud synchronization, online accounts, and repair policies. Even if research cases on older devices have been disclosed, this does not imply safety for the currently used primary device. This list does not cover vulnerability names, tool distribution sources, and installation sequences but addresses only the results indicated by manufacturer support documents and conditions that users need to verify.
If the goal is to enhance functionality, first check official repairs and cloud data options. Official channels are more likely to address similar demands while maintaining update and recovery support. If there is a separate purpose, such as preserving discontinued devices or conducting security research, laws regarding ownership, copyright, and access control can vary by country, necessitating professional verification before distribution or sharing. Devices containing work materials or payment information should be separated from experimental ones, and it’s advisable to back up important data separately, regardless of modification status.
기기 유형 휴대형 게임기
제조사 Nintendo
관련 시기 2019년
주요 위험 보증 제외·온라인 제한·기기 손상
공식 대안 공식 수리와 데이터 클라우드
Old devices like the Wii or 3DS and the currently critical online service dependent Switch cannot be viewed under the same criteria. Discontinued devices have preservation value, but issues with saved data and copyrights remain, and current devices can be affected by account, multiplayer, and purchased content.
First, check for genuine software, official data transfer options, and repair possibilities. If the device is used by children, it’s more practical to prevent unknown files and account sharing while utilizing parental controls rather than modifications for actual safety. Official policies and device-specific support may change, so it's safer to verify manufacturer guidance before use.
First, check for genuine software, official data transfer options, and repair possibilities. If the device is used by children, it’s more practical to prevent unknown files and account sharing while utilizing parental controls rather than modifications for actual safety. Official policies and device-specific support may change, so it's safer to verify manufacturer guidance before use.
한눈에 보기
7개
Nintendo DS Lite
휴대형 게임기 · Nintendo · 2006년 · 저작권 침해와 저장 데이터 손상 · 정품 카트리지와 공식 호환 정보
Nintendo DSi
휴대형 게임기 · Nintendo · 2008년 · 업데이트 충돌과 기능 정지 · 공식 시스템 설정과 구매 이력 관리
Nintendo 3DS
휴대형 게임기 · Nintendo · 2011년 · 계정·온라인·저장 데이터 위험 · 정품 소프트웨어와 데이터 이전
Wii
거치형 게임기 · Nintendo · 2006년 · 벽돌 현상과 저작권 문제 · 공식 디스크·호환 주변기기
Wii U
거치형 게임기 · Nintendo · 2012년 · 시스템 업데이트와 저장장치 충돌 · 공식 데이터 이전 및 호환 목록
Nintendo Switch
하이브리드 게임기 · Nintendo · 2017년 · 콘솔 사용 불능·계정 제한·저작권 위험 · 공식 e숍·자녀 보호·접근성 설정
Nintendo Switch Lite
휴대형 게임기 · Nintendo · 2019년 · 보증 제외·온라인 제한·기기 손상 · 공식 수리와 데이터 클라우드
이 포스팅은 쿠팡 파트너스 활동의 일환으로, 이에 따른 일정액의 수수료를 제공받습니다.
댓글 0
로그인 후 댓글을 작성할 수 있습니다.
첫 댓글을 남겨보세요.
이런 리스트는 어때요?


이런 리스트도 추천해요



🎲
여기서 멈추기엔 아쉽잖아?
다음에 뭘 볼지 고민하는 시간이 제일 아까워.
주사위가 대신 골라줄게 — 무슨 리스트가 튀어나올지는 굴려봐야 알지.
안 누르면… 평생 궁금하지 않겠어? 👀